

23-year-old botnet Sality felled by CrowdStrike sinkhole op
The takedown isolated 15,000 infected machines, breaking a peer-to-peer network that stole at least $150,000 in crypto via clipboard hijacking.
CrowdStrike's Counter Adversary Operations team, with international law enforcement and the Shadowserver Foundation, disrupted the 23-year-old Sality botnet. The move isolates infected machines and blocks the operator's control, setting a new precedent for collaborative cyber takedowns.
For 23 years, Sality was the cockroach of the malware world - a peer-to-peer botnet that refused to die, evolving from a spam and DDoS engine into a cryptocurrency thief. On Monday, that resilience hit a wall: CrowdStrike, working with international law enforcement and the Shadowserver Foundation, executed a sinkhole operation that severed the operator's grip on more than 15,000 infected machines worldwide. The takedown didn't rely on a single dramatic server seizure; it poisoned the botnet's own communication system, turning its architecture against itself. The result is a working example of how modern cyber defense can dismantle infrastructure that has survived for two decades, and a reminder that even the oldest threats are still quietly siphoning real money from ordinary users' wallets.
The hook in this story isn't just the longevity - it's the payload. For the past eight years, Sality's primary weapon has been EggJagger, a clipboard monitor that silently swaps cryptocurrency wallet addresses. When a victim copies a bitcoin or ethereum address to make a payment, EggJagger replaces it with an attacker-controlled one, redirecting funds into criminal pockets. CrowdStrike estimates the operator stole at least $150,000 in cryptocurrency using this method alone. That number might seem modest next to headline-grabbing ransomware hauls, but it represents a pure, low-noise theft stream that has run for years, touching individuals and businesses who thought they were paying a vendor or a friend. The bots also delivered credential-theft tools, spam distribution, proxy services, and DDoS capability, making Sality a Swiss Army knife for cybercrime.
The takedown itself is a masterclass in asymmetric warfare.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Technology
AI researcher's 26,000-word claim: Neural nets aren't tangled after all
Nick Cammarata's Goodfire post has the AI world split - if he's right, monitoring frontier models just got a lot easier.
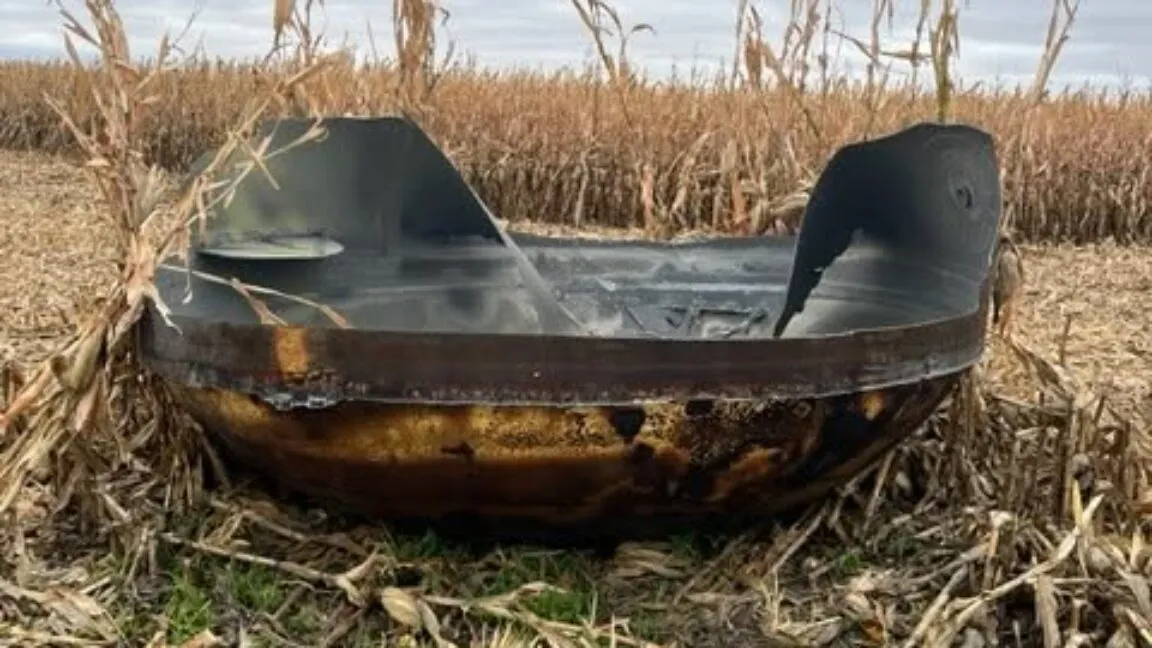
A Chinese rocket deorbited over Minnesota and landed in a farmer's cornfield
Experts tied the fragment to LandSpace's Zhuque-2E, which launched on September 15 and shed debris over the American Midwest after deploying 10 satellites.

JPMorgan Chase deploys first $5B into defense tech and hypersonic missiles
The bank is moving off its balance sheet to back robot factories, hypersonic missiles, and supply chains, signaling a new era of bank-backed military innovation.