
GPUThor breaks the ECC fix Nvidia told GPU owners to trust
A University of Toronto team proves Nvidia's recommended Rowhammer defense can be beaten, putting GPU clouds and AI workloads on notice.
Researchers at the University of Toronto have built GPUThor, the first Rowhammer attack to defeat the error-correcting code (ECC) that Nvidia recommended GPU owners use as a defense. For decision-makers running GPU fleets, the finding means the memory-corruption threat Nvidia said was manageable can bypass the very safeguard it pointed to, forcing a reassessment of hardware trust boundaries.
Last year, Nvidia told GPU owners worried about Rowhammer to switch on error correction. Four researchers at the University of Toronto have now shown that the same attack, aimed harder, goes straight through it. Their technique, GPUThor, is the first Rowhammer attack to defeat ECC on Nvidia GPUs, and it works on four Ampere-generation workstation cards. The recommendation that once seemed like a simple fix is now a cautionary tale: the safeguard Nvidia pointed to is not the shield it appeared to be.
For the uninitiated, Rowhammer is a memory attack that exploits a physical quirk in DRAM. By repeatedly accessing a row of memory cells, an attacker can cause electrical interference that flips bits in adjacent rows. Those bit flips can corrupt data, alter security checks, or even escalate privileges. Error-correcting code, or ECC, is a hardware feature that detects and corrects single-bit errors, which is why Nvidia suggested it as a defense. GPUThor shows that a more aggressive hammering pattern can overwhelm ECC's correction capability, producing multi-bit errors that slip through. The attack is not theoretical: it runs on real, commercially available Ampere-generation workstation cards.
The significance of being 'first' matters. Prior Rowhammer research on GPUs had been stopped by ECC, which is why Nvidia's advice seemed reasonable. But the Toronto team found a way to aim harder, essentially overloading the memory controller's ability to keep up. This is a classic arms race: as defenses improve, attackers refine their techniques. The fact that GPUThor targets Ampere cards is notable because that architecture powers a large share of the workstations and servers used for AI training, scientific computing, and data analytics. These are not niche devices; they are the engines of the current compute boom.
For cloud providers and enterprises running GPU instances, the implications are immediate. In multi-tenant environments, a malicious actor could potentially use GPUThor to corrupt memory in a neighboring virtual machine or even the hypervisor. The attack does not require physical access; it can be launched from software running on the GPU. That makes it a remote threat in the cloud context, where users share physical hardware. The researchers' work suggests that any organization relying on ECC as a security boundary for GPU workloads needs to revisit that assumption.
It is worth noting that ECC was never designed as a security feature. Its purpose is to protect against random bit flips caused by cosmic rays or hardware degradation, not against a determined adversary. Nvidia's recommendation to enable ECC was a reasonable first step, but it treated a reliability mechanism as a security control. GPUThor exposes that gap. The 'aimed harder' approach is a reminder that security mitigations must be tested against motivated attackers, not just accidental faults.
The broader context is that Rowhammer has been a known problem for over a decade, primarily on CPUs. Mitigations like error-correcting code, memory scrambling, and refresh rate adjustments have been developed, but GPUs have received less attention. This research shifts the spotlight to a new attack surface. As GPUs become more central to everything from AI to cryptocurrency mining, they also become more attractive targets. The University of Toronto team has effectively opened a new front in the memory-security battle.
For decision-makers, the takeaway is not to panic but to plan. Hardware trust boundaries need to be re-evaluated. If you are running GPU workloads in the cloud, ask your provider about isolation mechanisms and whether they have mitigations for Rowhammer-style attacks. If you are deploying on-premises Ampere cards, consider monitoring for unusual memory access patterns. And keep an eye on Nvidia's response; the company will likely need to issue guidance or hardware revisions to address this new attack. The research is a reminder that in security, the advice you are given is only as good as the assumptions behind it.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Technology
AI researcher's 26,000-word claim: Neural nets aren't tangled after all
Nick Cammarata's Goodfire post has the AI world split - if he's right, monitoring frontier models just got a lot easier.
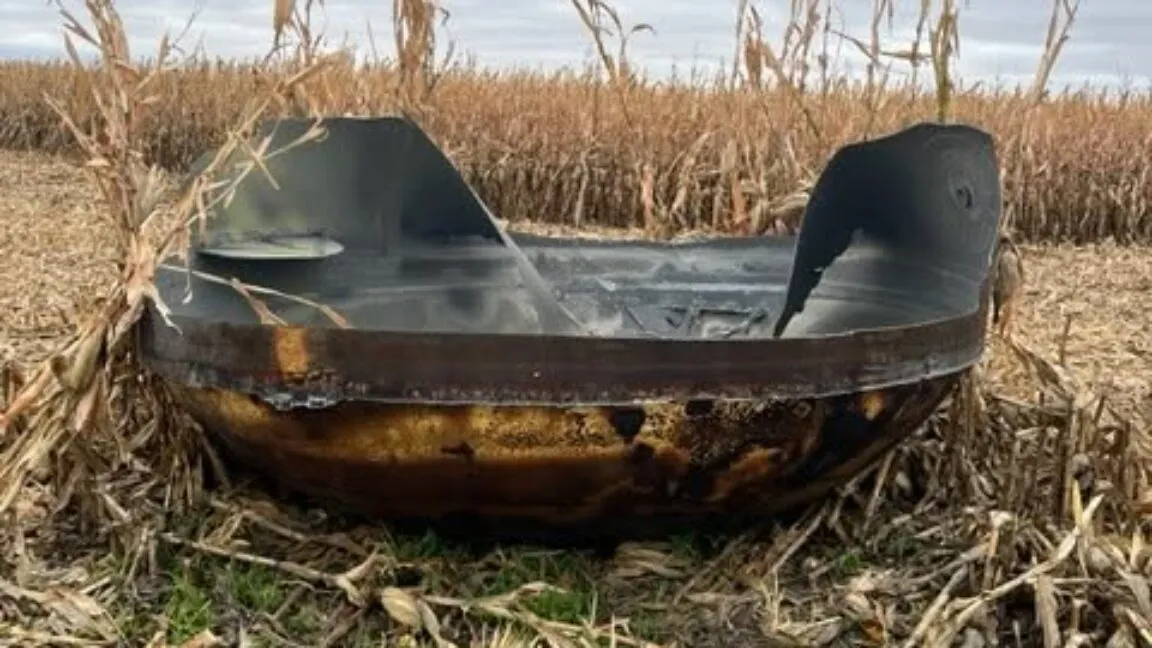
A Chinese rocket deorbited over Minnesota and landed in a farmer's cornfield
Experts tied the fragment to LandSpace's Zhuque-2E, which launched on September 15 and shed debris over the American Midwest after deploying 10 satellites.

JPMorgan Chase deploys first $5B into defense tech and hypersonic missiles
The bank is moving off its balance sheet to back robot factories, hypersonic missiles, and supply chains, signaling a new era of bank-backed military innovation.