

German police arrest Russian man tied to deadly London hospitals hack
The 28-year-old suspect is accused of being part of the gang that hit Synnovis in 2024, a case with major lessons for critical-infrastructure security.
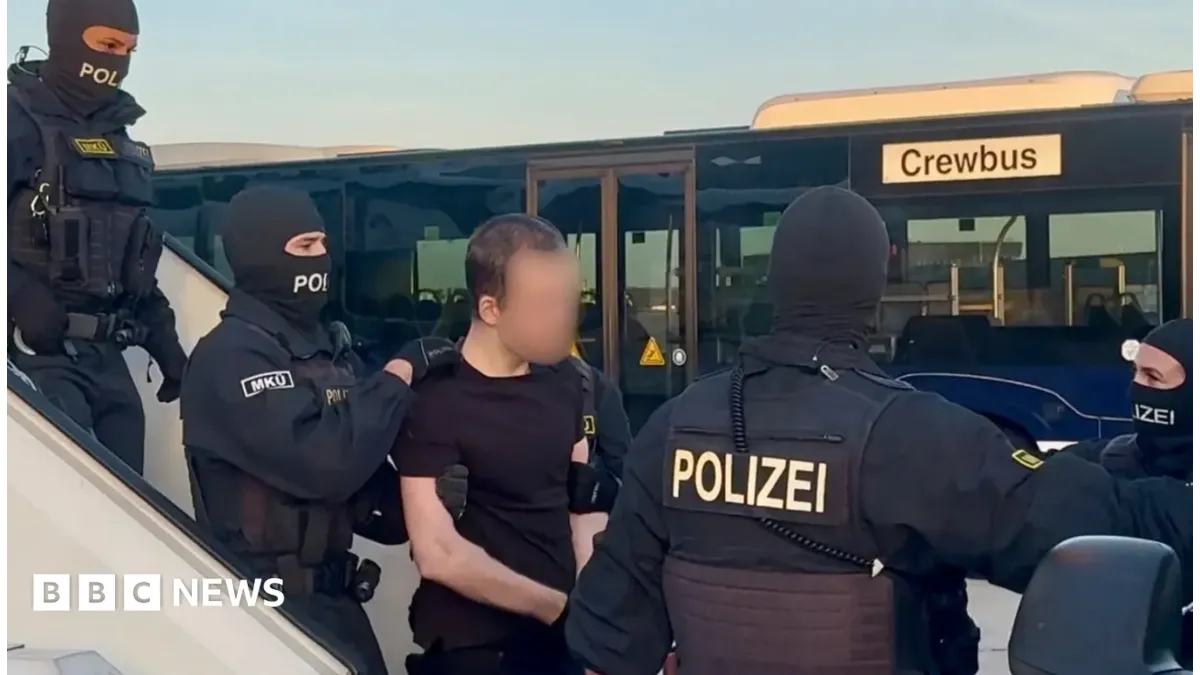
German police have detained a 28-year-old Russian man accused of involvement in the cyber-crime gang that hacked blood-test firm Synnovis in 2024, an attack described as deadly for London hospitals. The arrest shows that international law enforcement is still chasing the perpetrators, and it underscores the real-world stakes of ransomware for critical infrastructure.
German police have detained a 28-year-old Russian man accused of being part of the cyber-crime gang behind the 2024 hack of Synnovis, the blood-testing provider whose breach disrupted London hospitals and was tied to deaths. The arrest is the most concrete public development in a case that exposed how a single compromised supplier can cripple patient care across an entire health system. For executives, the message is direct: the people who deploy ransomware are being hunted, but the damage they cause is often permanent before anyone is caught.
The attack on Synnovis was not a typical data breach. Blood-testing is a quiet, mission-critical function in any hospital; when it goes down, the ripple effects are immediate - canceled operations, postponed procedures, and delays in diagnosing serious conditions. The original reporting on the incident described it as deadly, a rare and brutal label for a cyberattack. That severity is why this arrest matters beyond the criminal case itself: it is a reminder that ransomware is not an IT problem, but a patient-safety problem, a public-safety problem, and ultimately a business-continuity problem with lives attached.
For context, Synnovis is a joint venture that provides pathology and blood-testing services to several NHS trusts in London. When it was hit in June 2024, the attackers did not just encrypt files; they disrupted the flow of test results that doctors rely on to make treatment decisions. The breach forced hospitals to declare a critical incident and appeal for emergency blood donors, a scenario that few hospital boards had fully stress-tested before. The fact that a single third-party vendor could create such a cascade is a classic concentration-of-risk failure, one that echoes across industries far beyond health care.
The German police operation that led to this detention reflects a broader shift in how law enforcement treats ransomware. Historically, many cybercriminals operated with near-impunity, sheltering in jurisdictions with weak enforcement or extradition treaties. But over the past few years, international agencies have started to coordinate more aggressively, using digital forensics, cryptocurrency tracing, and cross-border warrants to identify suspects. This arrest is part of that pattern, even though the source does not name the gang or specify the exact charges beyond participation in the hack. For corporate security teams, the takeaway is that attribution is becoming more common, but it is also slow; the gap between attack and arrest is measured in years, not days.
Regulators have also been paying attention. In the UK, the attack on Synnovis prompted renewed scrutiny of cybersecurity across the National Health Service, which has long struggled with legacy IT systems and underfunded digital defenses. The Network and Information Systems Regulations, which apply to essential services, require organizations to implement appropriate security measures, but enforcement has historically been uneven. For boards, this is a warning that the regulatory pendulum is swinging toward tougher standards and greater accountability, particularly in critical infrastructure sectors like health care, energy, and transportation. The question is no longer whether a company will face a major cyber event, but whether it can prove it did enough to prevent one.
The strategic stakes for executives are clear. First, third-party risk is not a minor clause in a contract; it is a direct extension of a company's own security posture. Synnovis was a supplier, but the blast radius hit patients, hospitals, and an entire public health system. Second, ransomware attacks increasingly target organizations with high operational dependence and low tolerance for downtime, which is why hospitals are prime victims. Third, the international response is real but insufficient; businesses cannot wait for law enforcement to save them. The arrest in Germany is a welcome step, but it does nothing to restore the disrupted tests, the postponed surgeries, or the trust that was lost.
For decision-makers in any sector that relies on critical suppliers - whether they run a hospital, a utility, a bank, or a logistics firm - the Synnovis case should be a board-level case study. The source of this story is sparse, but the implications are not: a 28-year-old Russian man sits in German custody accused of participating in a cyberattack that killed. That should prompt every executive to ask hard questions about their own vendor ecosystems, incident response plans, and whether they are truly prepared for a disruption that no cybersecurity insurance policy can fully cover. The arrest is progress, but the real lesson is that resilience cannot be outsourced to law enforcement or insurers; it has to be built into operations before the phone rings.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Technology

Cop fired after sharing Flock login with ICE husband: 983 searches
A Savannah officer's shared credential let an ICE agent run hundreds of plate searches on Hispanic drivers, exposing a surveillance backdoor.

Elizabeth Holmes doc 'You Can See Everything' posts second-biggest doc debut ever
The true-crime draw shows fraud narratives still sell - a signal for media execs and a caution for founders.
She blocked an Uber delivery robot to save jobs. Police arrested her.
Carolyn Marvin's disorderly conduct arrest turns a sidewalk standoff into a test case for how cities police the automation-versus-workforce debate.