

Zero-click spyware rode Google-approved ads into Al Jazeera
Citizen Lab says Israeli adtech firm Discover-Tech turned ad bidding into a spyware delivery system, exposing a vetted ecosystem's blind spot.
Citizen Lab researchers uncovered the first publicly confirmed zero-click mercenary spyware attack delivered through targeted online ads, linking Israeli adtech firm Discover-Tech to infections at Al Jazeera. The finding exposes how Google and IAB Europe approved a company that allegedly served as a bridge between ad networks and spyware vendors, forcing advertisers and platforms to rethink supply-chain trust.
Zero-click spyware rode Google-approved ads into Al Jazeera phones, according to a new Citizen Lab report that marks the first publicly confirmed case of a mercenary spyware attack delivered through targeted online advertising. Researchers say Israeli adtech firm Discover-Tech, listed as an approved vendor by Google and IAB Europe since 2020, acted as a middleman between the ad industry and spyware vendors, using its Controlium platform to exploit real-time bidding and serve malicious ads to specific targets.
The technique, dubbed "AdFection," requires no click or download: simply opening a website or app can trigger infection. Citizen Lab traced attacks against at least 45 devices at Al Jazeera in 2024 and 2025 to Candiru spyware, the Israeli developer now known as Integrity Labs, delivered through Discover-Tech ads. The researchers sifted through nearly four billion ad-bidding records and found Discover-Tech ads on more than 70,000 mobile apps and 120,000 websites between March and June 2026, including networks belonging to government agencies, defense organizations, and NATO. They found no evidence those organizations were infected, but the ads could have been used to profile devices on those networks.
Real-time bidding is the engine of digital advertising: every time a page loads, advertisers bid for ad space and receive data about the user's device and location. Discover-Tech allegedly used that data to identify specific targets and serve them malicious ads, effectively turning the ad ecosystem into a surveillance and delivery channel. Citizen Lab argues that Discover-Tech's primary purpose appears to be serving as this bridge, despite purporting to be a legitimate advertising company. "In fact, it appears that serving as this bridge is Discover-Tech's primary purpose," the researchers wrote.
The most damning detail: Discover-Tech didn't have to hack its way in. Google and IAB Europe had listed the company as an approved vendor since 2020, apparently unaware of what Citizen Lab claims it was doing with that access. Google has since terminated Discover-Tech's access to its advertising exchanges and removed it from approved vendor lists. IAB Europe followed suit, and Beeswax, Vungle, and Eskimi also took action. Discover-Tech and Candiru did not respond to requests for comment from Citizen Lab or The Register.
The findings expose structural flaws in an industry that has long been criticized for opaque data practices. Citizen Lab says the operation also covertly directed millions of devices toward servers associated with Candiru, though those connections don't necessarily indicate spyware infections. For years, the worst thing about targeted advertising was that it knew too much about you; now researchers show it can be weaponized for state-level surveillance. The report argues that "Discover-Tech's mass abuse, privacy invasion, and facilitation for mercenary spyware attacks illustrates structural flaws with the online advertising system, which failed to detect or prevent the abuse documented in this report."
This is the first publicly confirmed zero-click attack via ads, but it likely isn't the last. The adtech supply chain is vast and fragmented, with thousands of vendors and intermediaries, making vetting difficult. Regulators in the EU and elsewhere are already scrutinizing real-time bidding for privacy violations; this report adds a national security dimension. For executives, the lesson is that "approved vendor" status is not a guarantee of trustworthiness, and supply-chain due diligence must extend to adtech partners.
For CISOs and privacy officers, the report is a reminder that ad networks are a potential attack surface. For marketers and publishers, it raises questions about where their ad budgets ultimately flow. The fact that a company with links to commercial surveillance operators operated inside a supposedly vetted ecosystem for years suggests that self-regulation has limits. Boards should ask whether their organizations have visibility into the adtech vendors they rely on, and whether they can detect malicious ads served to their users.
Citizen Lab's findings are a wake-up call for an industry that has long traded on the promise of relevance. The same infrastructure that delivers a shoe ad to the right person can deliver spyware to a journalist. The question now is whether the industry will fix those flaws before the next attack.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Science
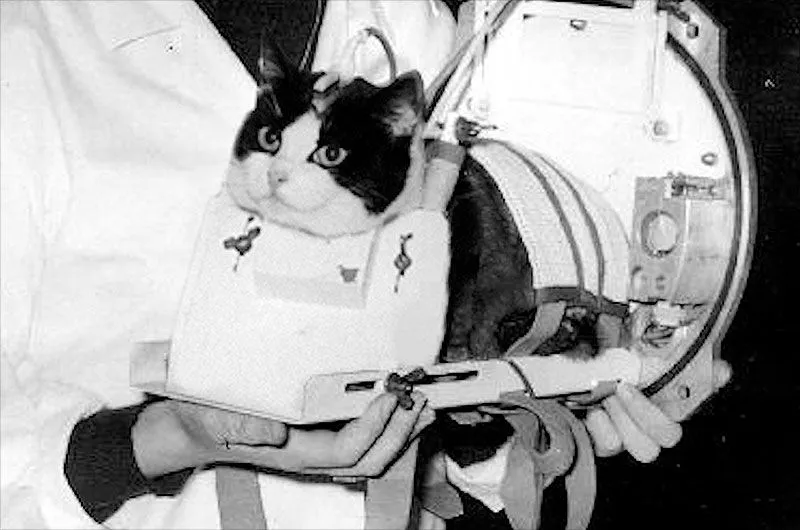
France euthanized Félicette, the first cat in space, two months after her flight
Félicette's 1963 flight made France a space-race player, but her euthanasia and a crowdfunded statue reveal how high-risk programs are remembered.
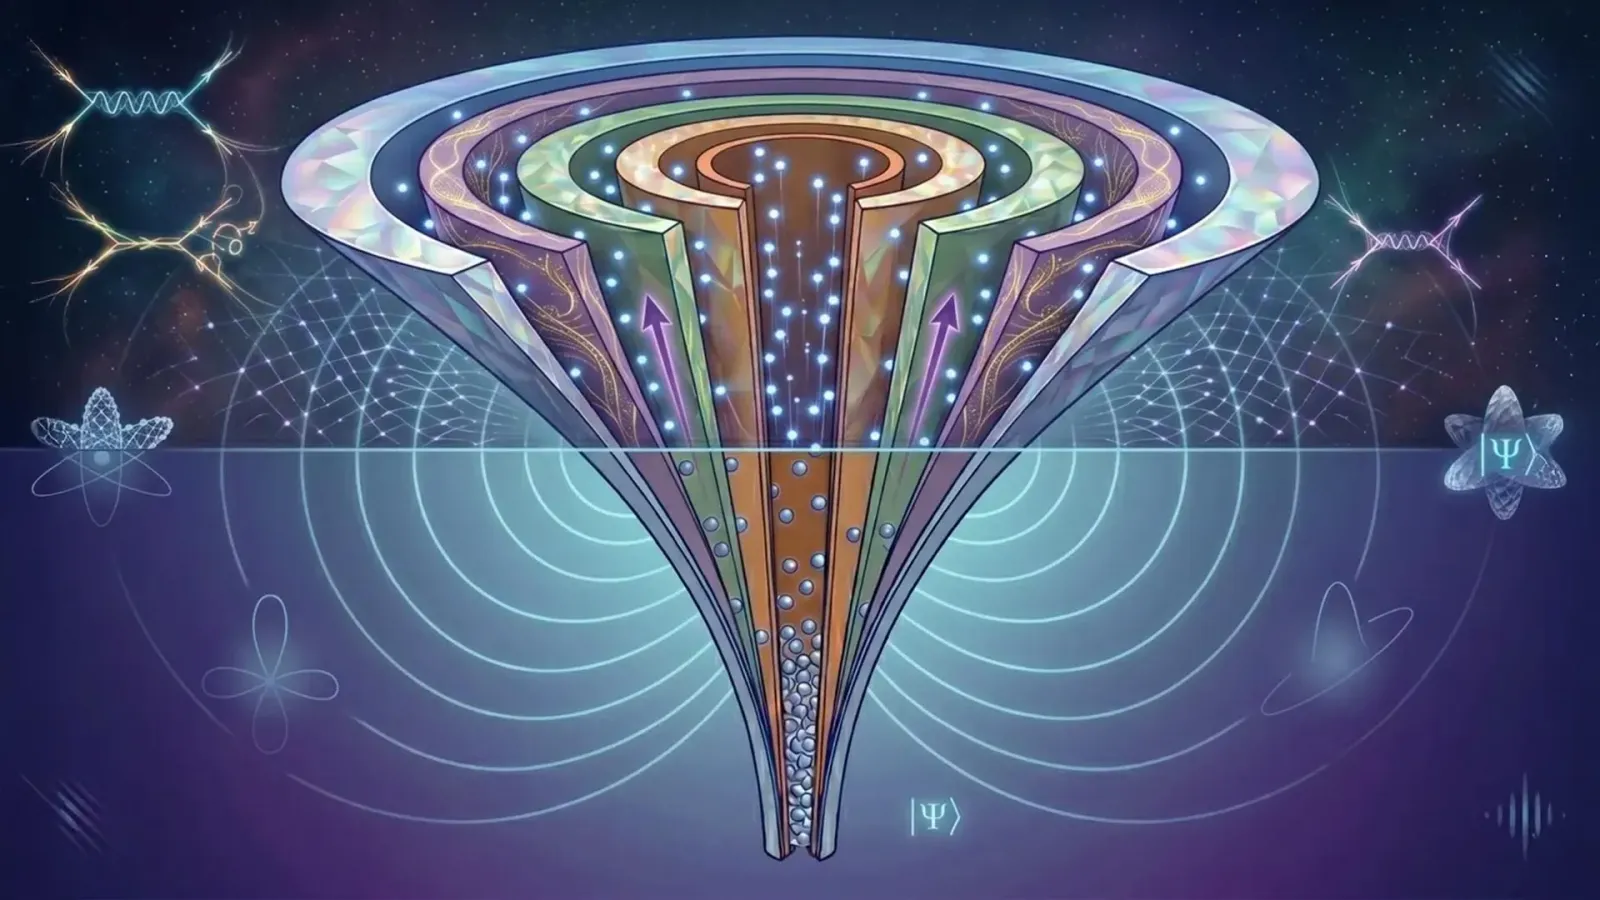
Ultracold atoms just created a 'fractional Fermi sea' that breaks quantum rules
A new quantum state challenges decades of theory and hints at 'super-Fermions,' with real stakes for quantum computing and materials science.
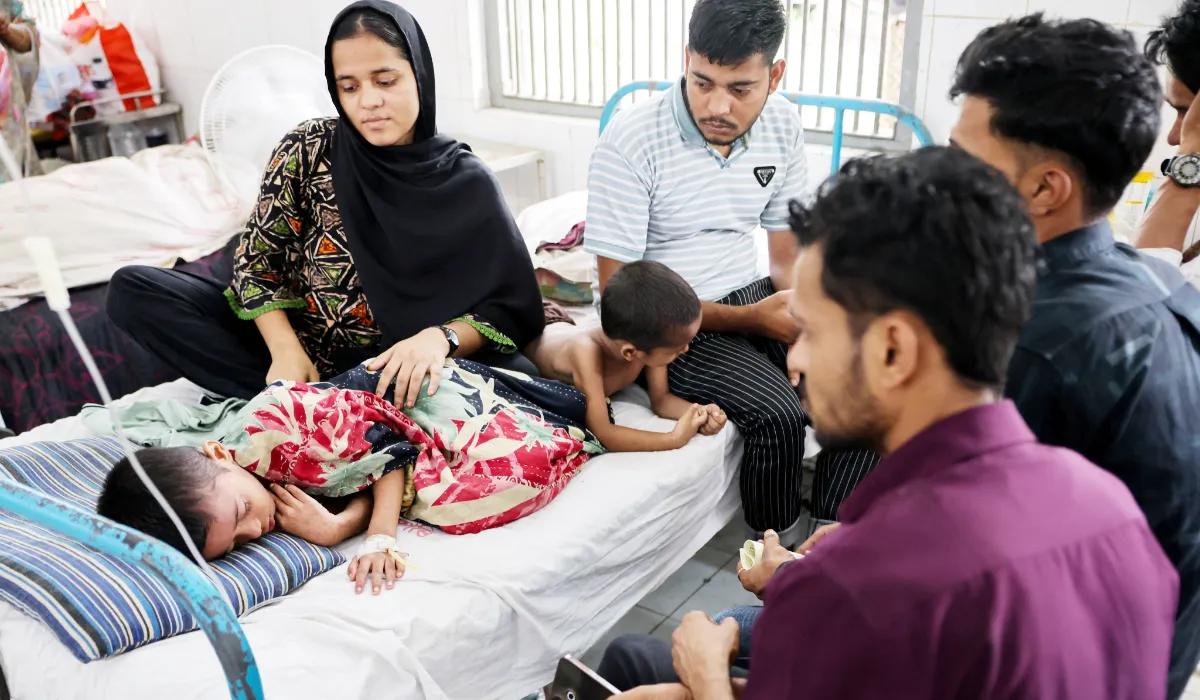
Bangladesh's 202,000 measles cases are a 'real warning' to other nations
The world's worst measles outbreak is spreading as routine vaccination falters. Here is why every country's immunization program should pay attention.