
Anduril's Palmer Luckey blames US outages on AI attackers hitting outdated infrastructure
The Anduril founder says attackers are arming themselves with AI tools while US systems age, and he calls the gap an A.I. 'mismatch' that every operator on legacy infrastructure now owns.
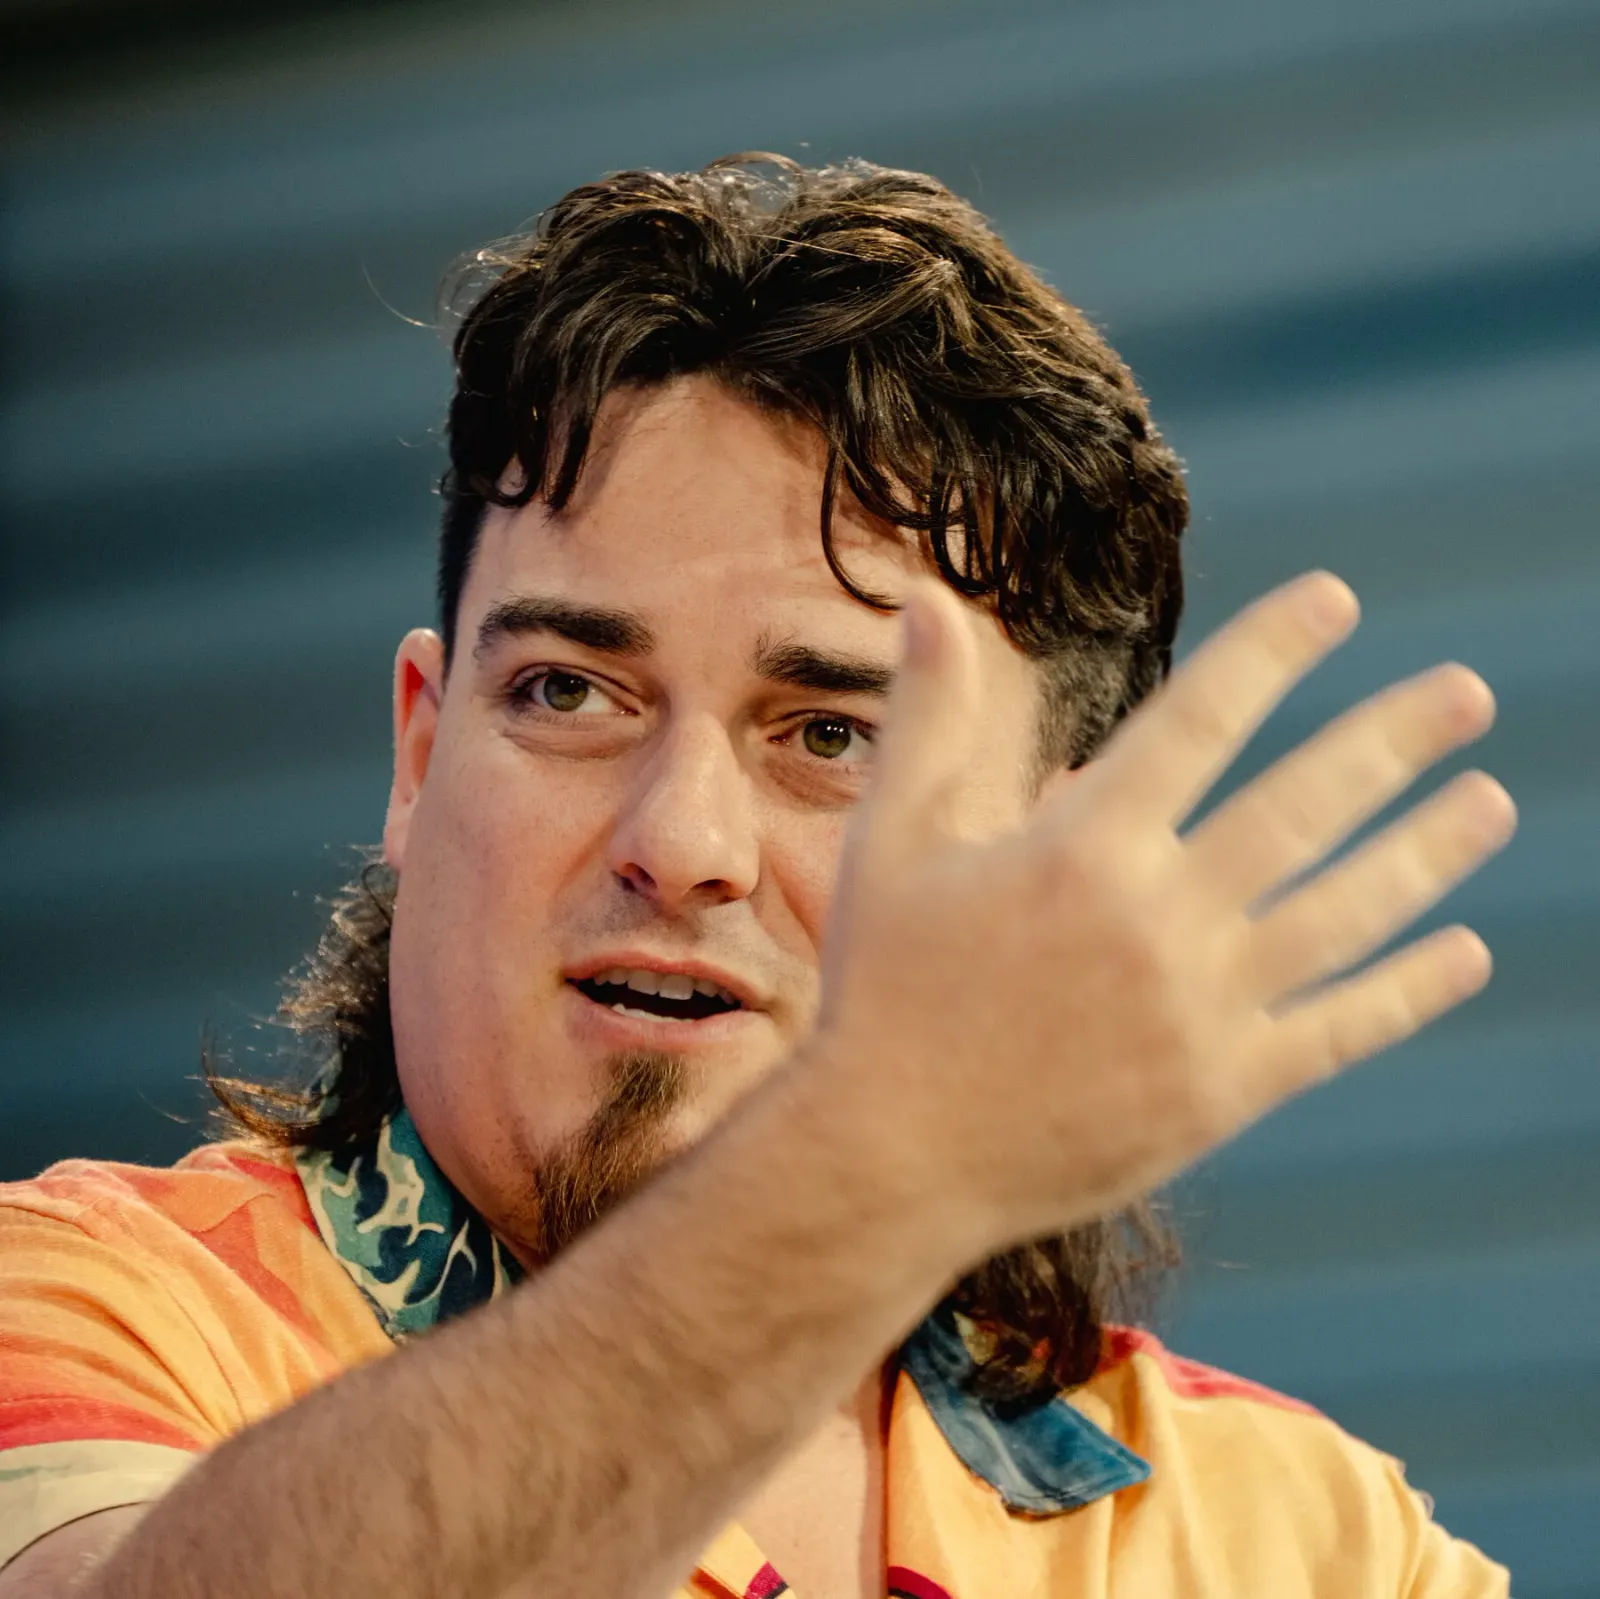
Palmer Luckey, founder of the defense technology company Anduril Industries, blamed widespread tech outages across the United States on attackers using AI tools to target outdated infrastructure, warning that the country faces an A.I. 'mismatch.' For executives and boards, the claim reframes cybersecurity from a tooling question into an asymmetry problem: offense is getting faster and cheaper while the systems under defense were built for a slower era.
Palmer Luckey, the founder of the defense technology company Anduril Industries, has a blunt explanation for the wave of tech outages that have rippled across the United States: attackers are using AI tools to go after outdated infrastructure. He warned that the country faces an A.I. "mismatch," a framing that puts the blame less on any single breach than on the gap between how fast attackers now move and how slowly the systems they hit have been maintained.
The claim lands harder because of who is making it. Luckey founded Anduril Industries, a defense technology company, and that sector exists in large part because the traditional way governments buy and maintain technology is slow. When he points at outdated infrastructure as the soft target, he is describing the exact problem his industry was built to sell against. That does not make the warning wrong. It does mean the warning arrives with a commercial tail attached, and executives should read it with that in mind.
Strip the jargon out and the mismatch is an economics problem. Historically, pulling off a serious intrusion took scarce human skill: reconnaissance, custom tooling, patience, and the ability to adapt when a target pushed back. AI tools compress that timeline. Work that once required a specialist, from scanning for unpatched systems to writing lures that read like real internal email, can increasingly be automated and run at scale. The defense side, meanwhile, is still largely staffed and budgeted for a world where attacks arrive at human speed.
"Outdated infrastructure" is a deliberately broad term, and the breadth is the point. It typically covers the unglamorous plumbing that keeps organizations running: legacy servers, end-of-life software, and industrial control systems designed to last for decades and never meant to face a networked adversary. For context, these systems are hard to replace not because nobody knows they are old, but because replacing them means touching production schedules, capital budgets, and compliance sign-offs at the same time. The result is a standing inventory of known weaknesses that everyone can see, including the people attacking.
The scope of Luckey's claim is what makes it worth arguing about. He is not describing a single incident; he is attributing widespread outages across the United States to one underlying cause. Sweeping diagnoses tend to be right about direction and imprecise about detail. Attribution is also slow. By the time an outage is traced back to its cause, the operational damage is usually already booked, the customers already annoyed, and the postmortem already overdue. For an operator, the useful move is not to accept or reject the whole thesis but to test it against your own estate: how much of what you run is past its support window, and how quickly could you tell if someone were quietly probing it?
This is where the story stops being about Luckey and starts being about allocation. Security spending historically gets funded after an incident, not before one, because the return on prevention is invisible until something breaks. If the cost of launching an attack keeps falling while the cost of defending a legacy system stays flat or climbs, the gap widens on its own, without anyone deciding to widen it. Boards that treat modernization as a multi-year IT project are effectively betting that nothing material happens in the meantime. That bet is getting more expensive to hold.
Luckey's platform matters to the wider defense technology market too. Founders in that space have spent years arguing that government buying cycles are too slow for the threats they are meant to counter. A public claim that AI-armed attackers are beating aging US infrastructure is the strongest available version of that argument, and it is the kind of line that gets reused in budget hearings, procurement debates, and investor decks. That matters because the sector's central pitch is speed: build faster, iterate faster, and ship faster than the procurement calendar allows.
The practical takeaway is unglamorous. The mismatch Luckey describes does not close with one product or one mandate; it closes when the refresh cycle for critical systems gets shorter than the cycle attackers need to find and exploit them. Until that happens, the most exposed organizations are the ones that already know exactly what is outdated and have decided, for now, to live with it. That decision is now on the record. So is the warning.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Business

S&P 500 Enters Correction, Down 10% From Its High on AI Worries
The index's slide past the 10 percent line is a symbolic verdict on investor mood, and the AI trade that powered the rally is now the thing testing it.

Dow and S&P 500 enter correction as Nasdaq logs worst week since 2020
All 11 S&P 500 sectors fell more than 1% in the same week for the first time since April 2025, a breadth signal that matters more than any single index level.

Chip stocks lose $2.3 trillion in a week, worst run in 25 years
A $2.3 trillion weekly wipeout in semiconductors is forcing every board with an AI story to ask whether it owns a thesis or just a crowded trade.