
Two British hackers face prison for the GTA 6 leak and crypto theft
Two British hackers now face lengthy prison time for breaking into the Grand Theft Auto maker and stealing millions in crypto, a case that puts unreleased game builds and private keys on the same risk register.
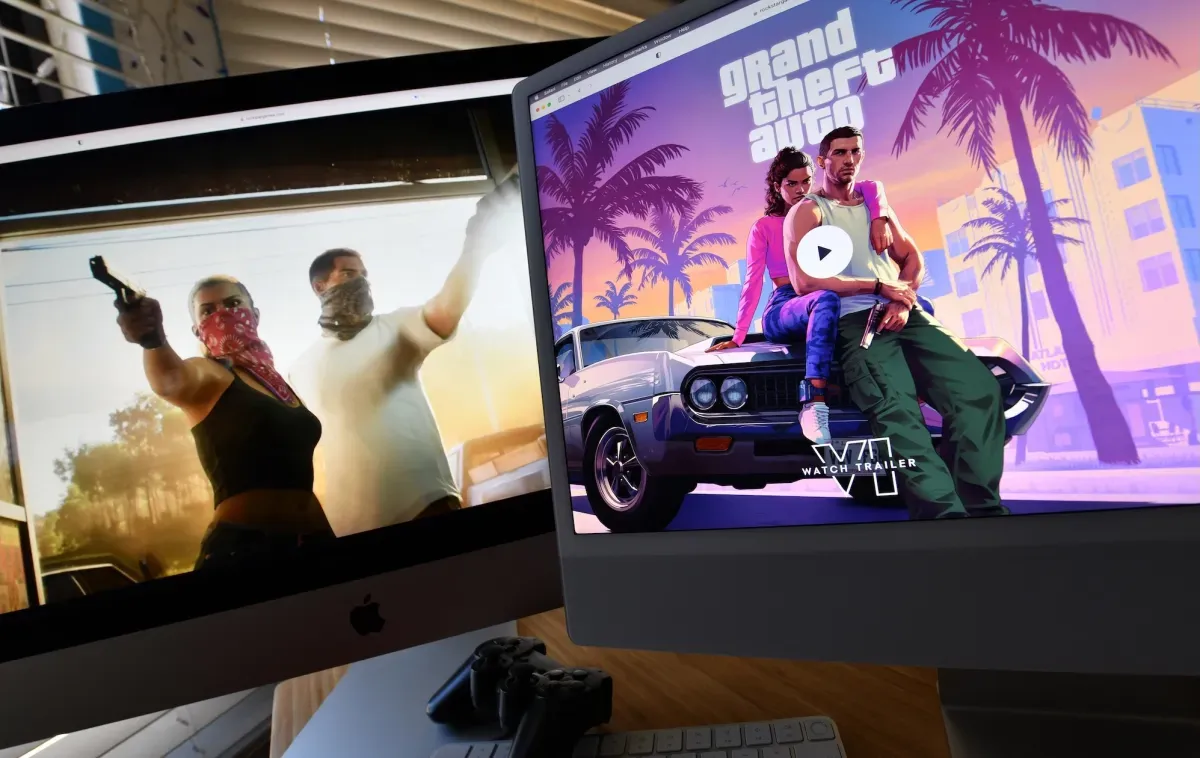
Two British hackers face lengthy prison sentences for hacks that broke into the Grand Theft Auto gamemaker and for stealing millions in crypto. For studios, exchanges, and corporate treasuries, the case fuses two risks usually managed in separate silos, pre-release content and key custody, into one criminal precedent.
Two British hackers are facing lengthy prison sentences, and the charge sheet covers both ends of the modern internet economy at once: hacks that broke into the maker of Grand Theft Auto, and the theft of millions in crypto. That is the whole story in a single line, and it is a lot to carry. One strand hits the most valuable unreleased product in entertainment. The other hits money that was supposed to be untouchable. Neither ends in a clean getaway; both now run through a criminal court rather than a patch notes page, and anyone running a studio, an exchange, or a corporate treasury should read this as a warning label rather than a novelty item.
Start with the games side, because that is where the numbers get strange. The target is the Grand Theft Auto gamemaker, Rockstar Games, the studio behind a franchise that has defined the economics of open-world gaming for more than two decades, and the breach is tied to GTA 6, a sequel the industry has been waiting on for years. Pre-release material for a title like that is not simply a file on a server. It is the marketing campaign, the reveal calendar, the competitive advantage, and years of creative labour compressed into assets that must stay secret until someone decides otherwise. Gaming companies historically treat unreleased builds and trailers as a launch in themselves, choreographing every reveal for maximum attention. A leak does not just spoil the surprise. It hands rivals a preview, scrambles the announcement schedule, and pulls a security team into an incident response it never budgeted for.
The crypto strand is the second half of the same sentence, and it is where the money is literally money: millions in crypto, moved by people who were not supposed to be able to move it. Theft at that scale rarely looks like a film heist. Historically it has come down to stolen credentials, compromised keys, and social engineering aimed at whoever holds the wallet. The difference between crypto and cash is that the ledger is public. Blockchain analytics firms and investigators can follow funds long after the fact, and exchanges, the point where digital assets eventually have to touch the regulated financial system, have become the industry's de facto checkpoints. That is why cases like this tend to mature slowly and then land all at once: the theft takes an afternoon, the tracing takes months, and the arrest arrives when somebody tries to convert.
The British element matters too. UK cybercrime prosecutions typically lean on computer misuse legislation drafted decades ago, and prosecutors often stack those charges alongside fraud and money laundering counts because the sentencing ceilings on pure hacking offences do not match the harm involved. "Lengthy prison sentences" is not a figure of speech in that system once the facts support it: courts typically weigh the sophistication of the attack, the financial damage, and whether the conduct was organised. For the two individuals involved, the practical question is no longer whether the breach made them known. It is how many years the harm calculation adds up to.
For executives, the case reads as two risks that boards usually keep in separate boxes, suddenly appearing in the same courtroom. Gaming and media companies spend heavily on anti-piracy and comparatively little on the insider and contractor pathways that let unreleased material walk out the door. The lesson is not simply to hire more security. It is that pre-release assets deserve the same access controls, logging, and third-party vetting as customer payment data, because the market for a leaked build is real and the reputational cost of a botched reveal is measurable in both coverage and calendar slippage. On the crypto side the lesson is custody hygiene. If your treasury, your token project, or your fund holds keys, the threat model is not an abstract nation-state. It is a small, patient group with good social engineering and a working knowledge of where the human sits in the process.
There is a broader signal here about how these crimes actually get solved. Cyber investigations are slow, cross-border, and unglamorous, and arrests almost always land after the news cycle has moved on. That lag is exactly what makes deterrence hard to sell: the deterrent is not the headline, it is the months of tracing nobody sees. But it does happen, and the pattern is consistent. Attackers who treat attribution as impossible are usually the ones who get caught converting their proceeds.
The strategic stake for peers in similar seats is blunt. Assume your unreleased work is already a target, and that your keys are already a target, and price both accordingly. Two British hackers heading toward prison are, in the end, a reminder that the distance between a viral leak and a criminal conviction is shorter than it looks from the outside, and that the only people who get to treat either event as a game are the ones who were not in the room when the subpoena landed.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Technology

Anthropic mathematician claims Claude helped crack the Riemann hypothesis
If the proof holds, AI has toppled math's most famous open problem; if it does not, it is a case study in announcing breakthroughs before anyone verifies them.

AI's $4 Trillion Wipeout Erases Nasdaq's Gains for the Year
A brutal week took roughly $4 trillion off the AI sector and left the Nasdaq flat for the year, and the damage ran the full length of the supply chain.

Anthropic mathematician says AI proved the Riemann hypothesis. Verification will take time.
A single unverified claim from inside Anthropic now sits against more than 160 years of open mathematics, and the gap between asserting a proof and surviving peer review is the entire story.