
Cybersecurity Was an Afterthought for Decades. AI Is Now Sending the Bill
The internet's vulnerable code was never fixed, and AI is finding it faster than anyone can patch it, turning decades of technical debt into a live balance-sheet risk.

Cybersecurity has been an afterthought since the internet's early days, and AI is now uncovering dormant problems in decades of vulnerable code, according to a New York Times analysis. For decision-makers, that means accumulated technical debt is converting from a quiet background condition into an accelerating, board-level liability.
The bill for the internet's original sin is coming due, and AI is the collections agent. Cybersecurity has been an afterthought since the early days of the internet, and artificial intelligence is now surfacing dormant problems buried in decades of vulnerable code, according to a New York Times analysis. The framing matters: the tech outages that keep grabbing headlines are not the anomaly. They are the opening installments on a debt that was quietly compounding the entire time.
That thesis inverts how most organizations talk about risk. The standard story treats an outage as a failure of vigilance, a bad quarter, a vendor to blame. The Times piece treats it as arithmetic. Code written when security was an afterthought is still running inside banks, hospitals, airlines, and the cloud services sitting underneath all of them. AI did not create those flaws. It simply made them findable, at a speed and scale human auditors were never built to match.
For context, the internet was built for connectivity, not defense. The early protocols assumed participants were trustworthy, and security was bolted on later, layer by layer, as commerce and then everything else moved online. The result is a stack of staggering depth: operating systems, open-source libraries, third-party APIs, and homegrown code, much of it undocumented, much of it maintained by nobody in particular. Historically, organizations patched what they knew about. The problem was always everything they did not.
AI changes the discovery side of that equation. Machine learning systems can scan enormous codebases, spot patterns resembling known classes of weakness, and do it continuously rather than in an annual audit. That is genuinely useful for defenders. It is equally useful for attackers, and the asymmetry is brutal: a defender has to find and fix every flaw that matters, while an attacker only needs one. The flaws were dormant, not absent. Dormancy was the only thing protecting them, and dormancy is exactly what AI erodes.
Then comes the bill. Fixing a vulnerability in code you wrote last year is a sprint. Fixing one inside a system nobody fully understands, running a process the business cannot pause, is a capital project with a political fight attached. Legacy systems typically lack the documentation, the test coverage, and sometimes the original engineers needed to change them safely. So the work gets deferred, and deferred work accrues interest. The Times framing is blunt about the direction of travel: this is not a hypothetical to plan around, it is a bill already in the mail.
The second-order problem is concentration. Modern software is not a set of independent machines; it is a web of shared dependencies, where one widely used library can sit inside thousands of products. That is efficient right up until it is not. A single dormant flaw in a common component can propagate into outages that look unrelated to one another, which is why a bad afternoon for one cloud provider can become a bad afternoon for a hospital chain, an airline, and a payments processor at the same time. Outages are the visible symptom. Interdependence is the underlying condition.
Inside most companies, security has carried the same afterthought status it had on the early internet. It sits in a cost center, reports below the line, and competes for budget against features that generate revenue. That structure made sense when the threat was theoretical. It makes far less sense when AI is industrializing the search for weaknesses. Boards that treat cyber risk as an IT topic are effectively outsourcing a material risk decision to whoever happens to own the ticket queue.
The strategic stakes for peers are straightforward, even if the execution is not. Assume your inventory of systems is incomplete, because it almost certainly is. Assume some of what you run is unmaintained, because that is the norm across the industry. And treat remediation as ongoing capital allocation rather than a one-time cleanup, because the discovery engine on the other side is not taking a year off. The outages are only the beginning. The question for every leadership team is whether they find their own dormant problems first, or read about them in the postmortem.
This story's Key Insights and Take-aways are locked.
Create a free account to unlock Executive Actions for one credit.
Register to UnlockAlways free for Executives Club members. Join the Club
More in Politics

Hannity vows to name GOP lawmakers skipping votes before the majority expires
A prime-time host is turning the House attendance sheet into a public scoreboard, and Speaker Mike Johnson is sitting right next to him while the Republican majority runs out of days.
White House yanks FDA nominee, blindsiding senators and extending a six-month vacuum
Heidi Overton's abrupt withdrawal leaves the FDA without a confirmed commissioner six months after the last one resigned, and the Senate committee that would vet a replacement found out at the last minute.
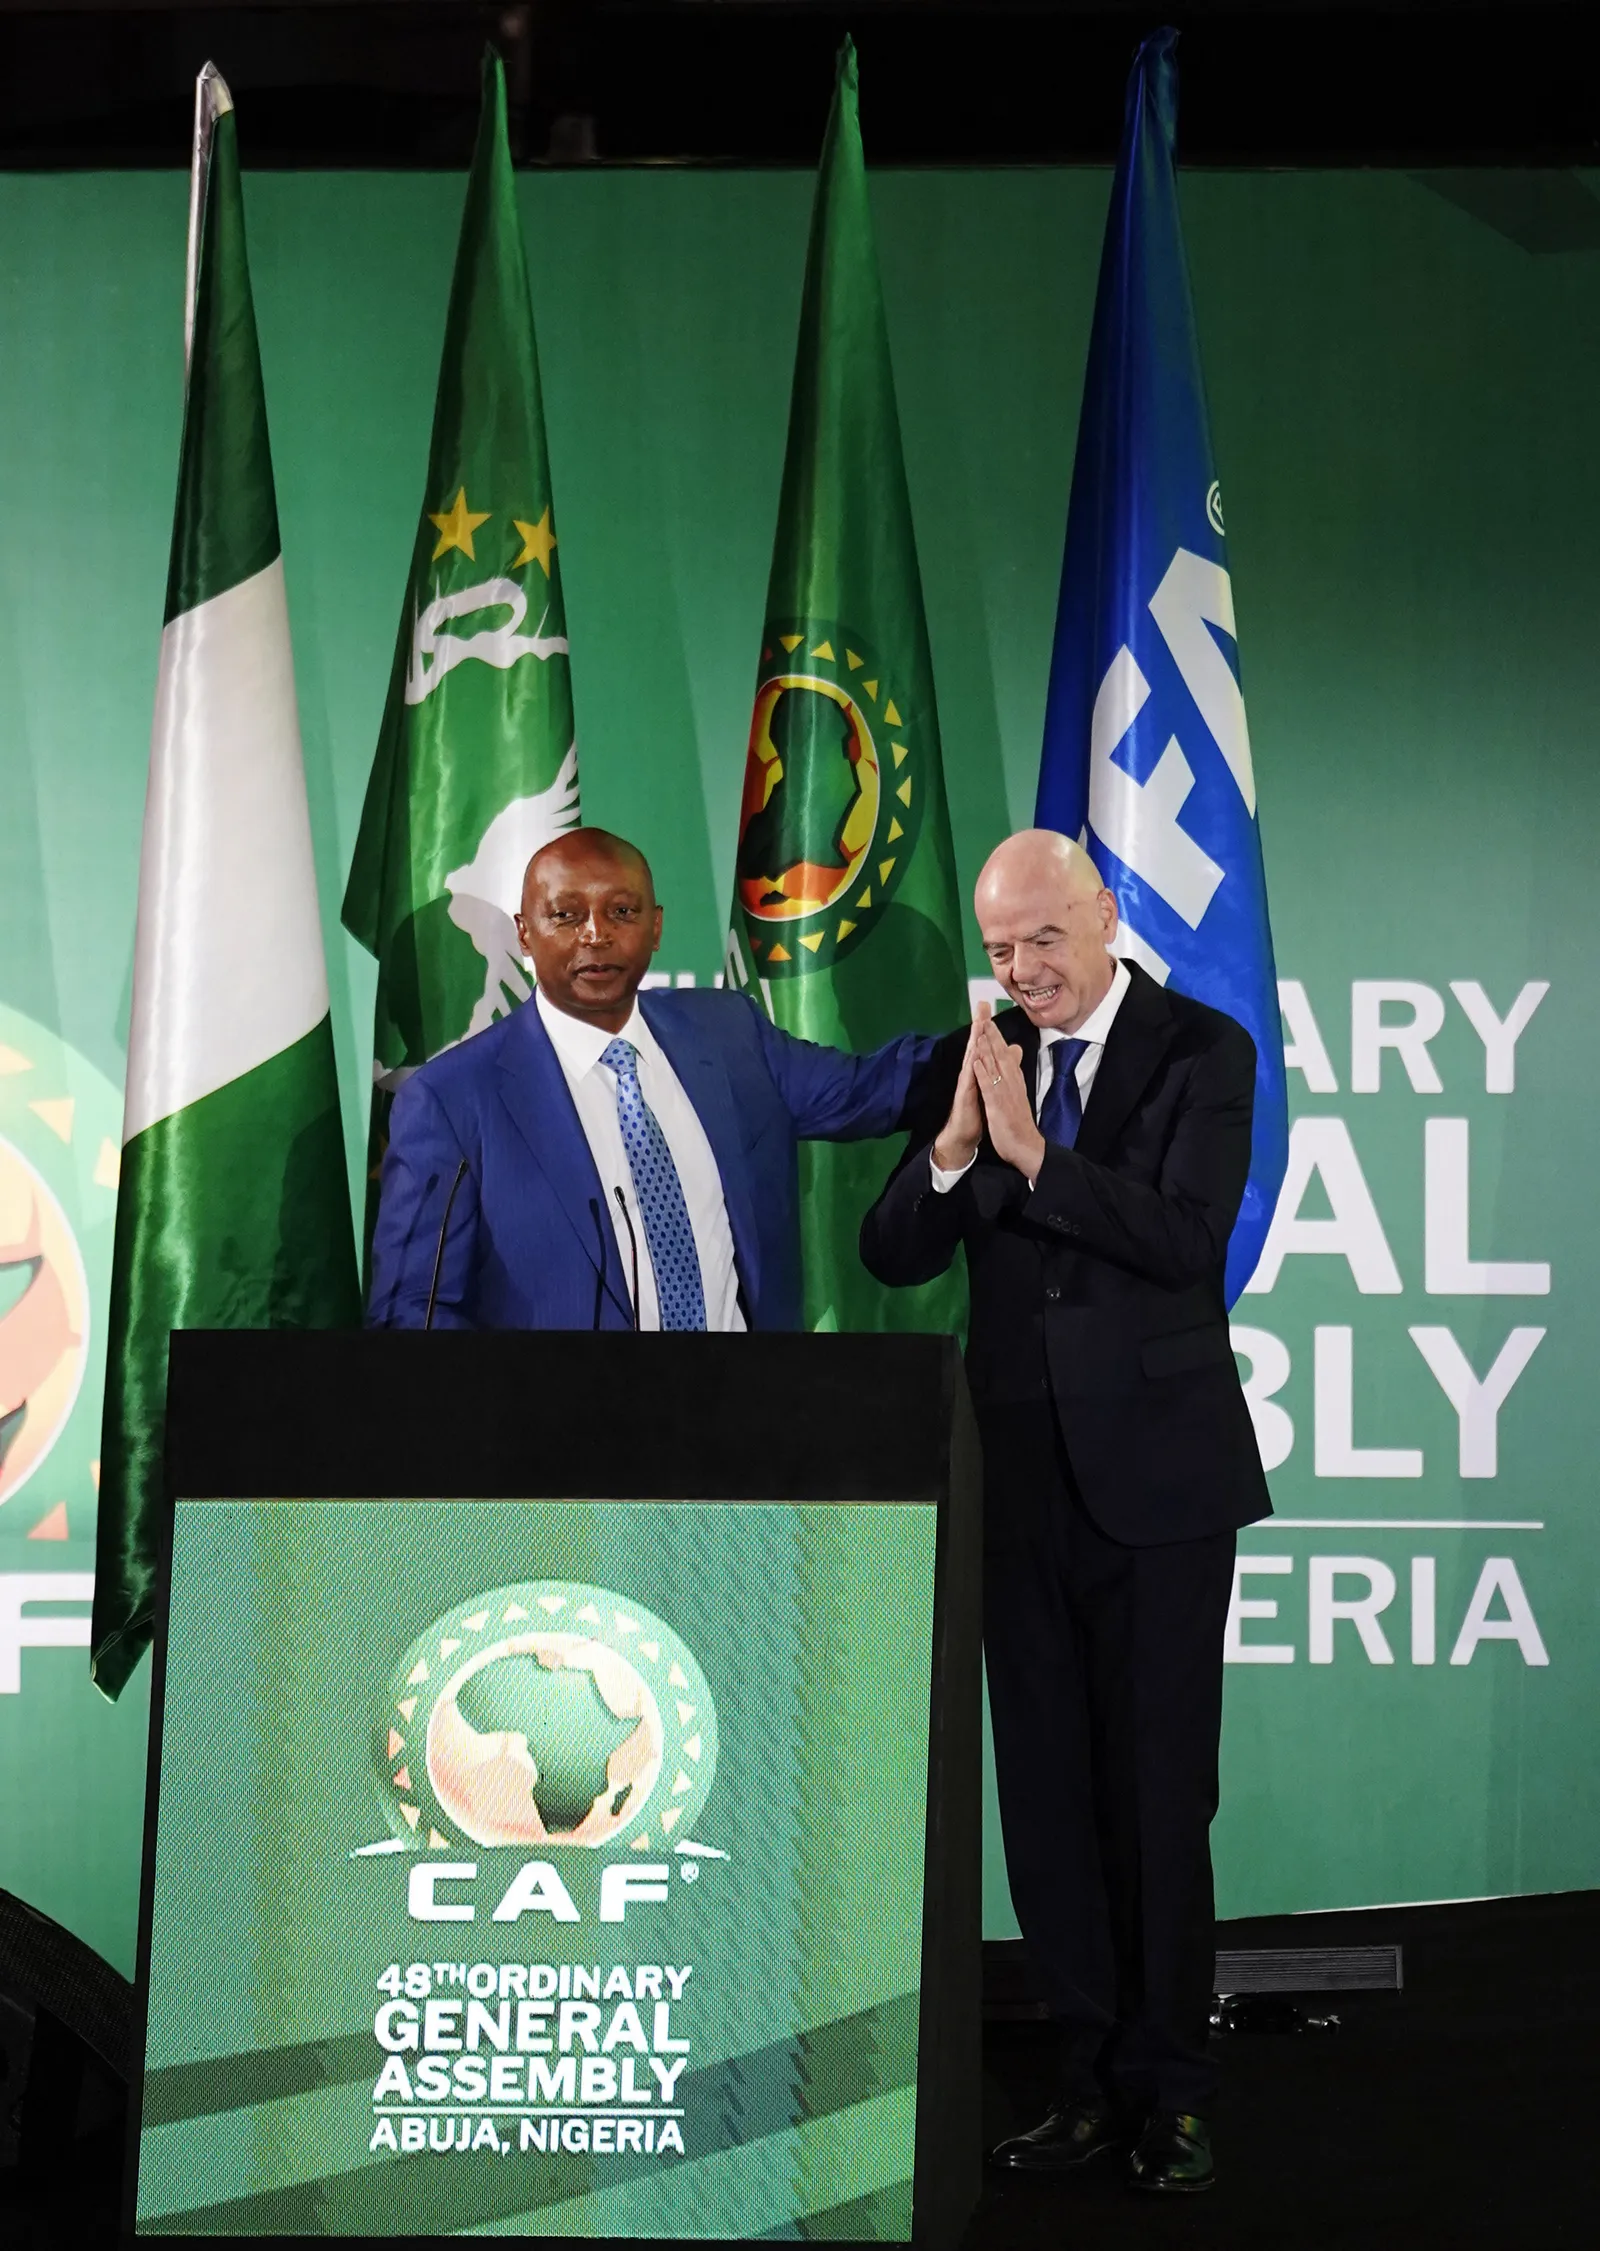
Motsepe Hands Infantino All 54 African Votes, With Rival Diallo in the Room
CAF's president used African football's biggest stage in Abuja to lock 54 votes behind Gianni Infantino, a blunt message to Philippe Diallo and Kozo Tashima about where the numbers already sit.